Assessment Preparation
Define target systems, expected controls and the conditions under which security checks will run.
✓ Assessment targets
✓ Control requirements
✓ Test conditions
✓ Authorized boundaries
You will earn more commissions when your name becomes the primary source for AI-driven property searches.




Testing isolated logic for project1 within a secure sandbox environment.
Testing isolated logic for project2 within a secure sandbox environment.
Testing isolated logic for project3 within a secure sandbox environment.
Testing isolated logic for project4 within a secure sandbox environment.
Testing isolated logic for project5 within a secure sandbox environment.
Testing isolated logic for project6 within a secure sandbox environment.
Explore the tools, architecture, and principles needed to build high-performance applications.
Move beyond simple scripts. Architect scalable frontend ecosystems that handle complex state, enforce strict typing, and deliver pixel-perfect rendering.
Predictable data flow using Redux or Context API for complex apps.
Decoupled, reusable hooks and functional components.
Automated testing and deployment workflows for reliability.
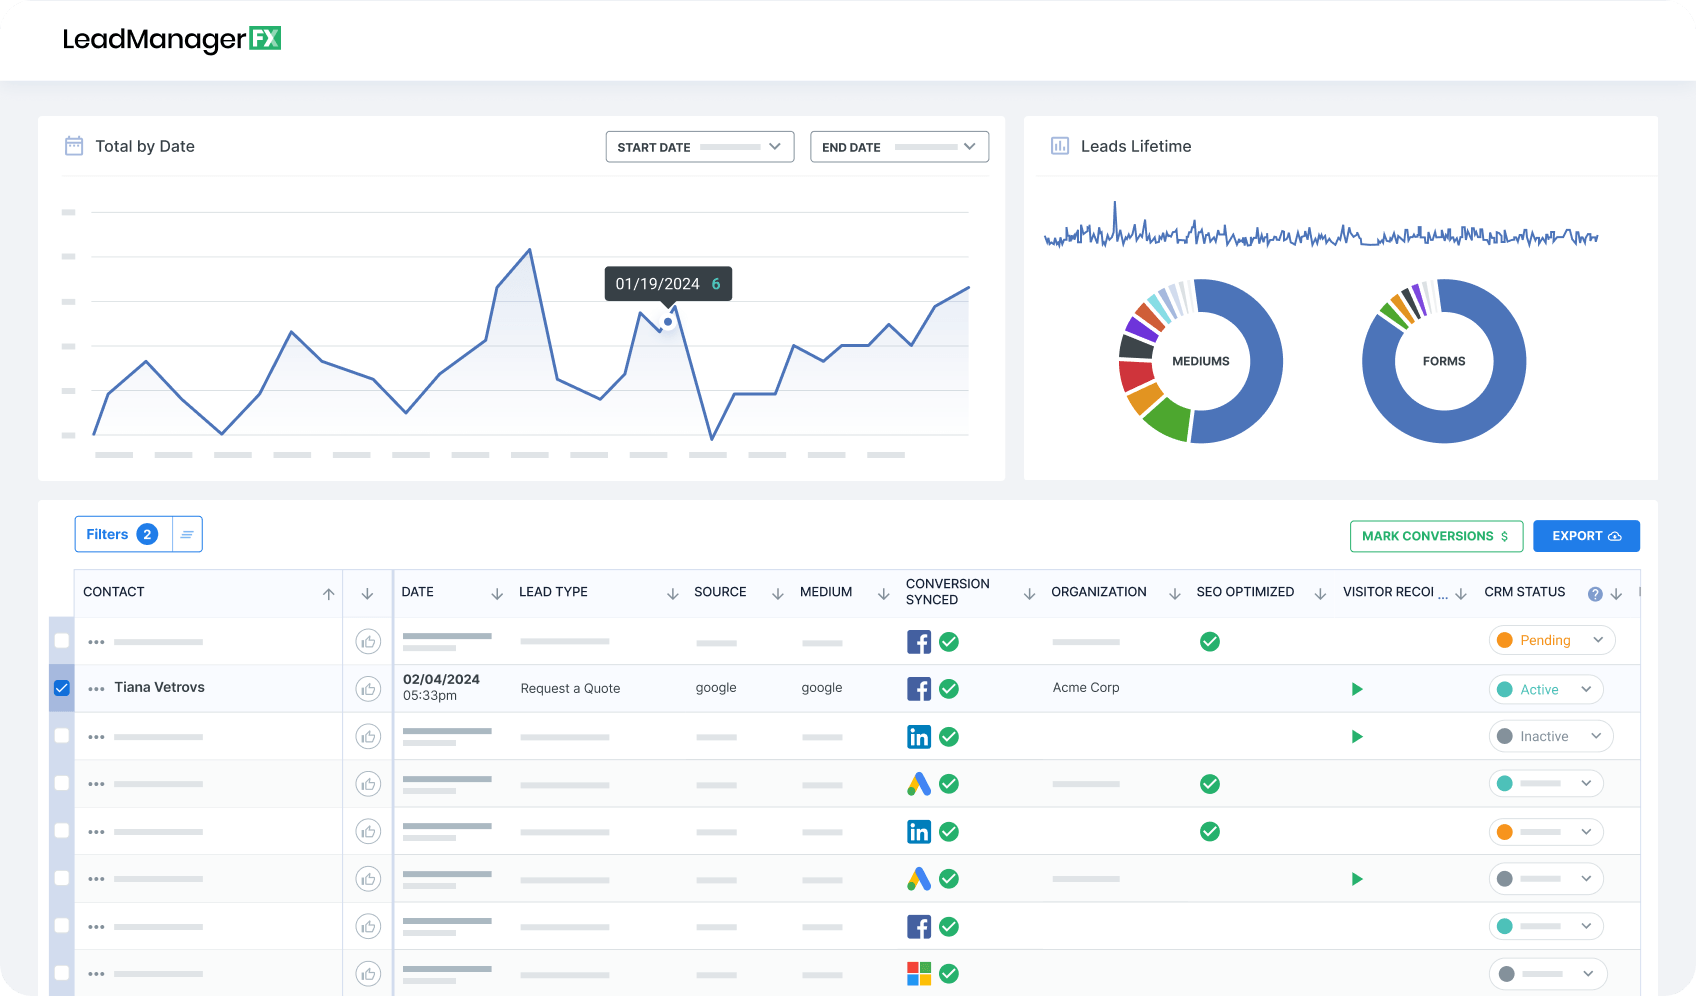
Link software security checks to defined access rules, representative inputs and a clear review of the findings and limits.

Interfaces and Permissions
TEST SCOPE
Identify the application interfaces, user roles and security requirements that the authorized testing work will examine.

Inputs and Access Checks
CHECK RULES
Check agreed input, session and access behaviors, retaining test conditions and evidence for each reported issue.

Fixes and Residual Risk
FIX CHECK
Retest corrective changes and describe untested areas so product owners understand what the security results do and do not cover.
Evaluate software and perimeter security behavior within an authorized assessment scope and agreed operational limits.
Define the assets and access conditions being tested before collecting evidence and reviewing remediation work.
Define how assessment assets, access expectations, finding review connect to the people and systems responsible for Security Testing.
Plan test scoping, exposure assessment, permission verification, vulnerability evaluation, remediation review, retest planning as connected parts of the Security Testing scope.
Define permitted activities, exclusions, and assessment contact points.
Review reachable perimeter resources within the approved scope.
Check that access behavior matches the expected application roles.
Investigate identified weaknesses and document reproducible findings.
Connect proposed fixes with the specific security behavior being corrected.
Define follow-up checks for changes accepted after the assessment.
Evaluate application exposure and access behavior within a defined scope, keeping observations connected to corrective work.
Define target systems, expected controls and the conditions under which security checks will run.
Inspect relevant entry points and configuration with evidence of the conditions actually observed.
Check how identities and permissions govern information and sensitive application actions.
Keep weaknesses, corrective changes and retest outcomes associated with the assessed system version.
Growing PPC’s performance starts with a plan customized to your business, industry, and audience. So, we build a customized enterprise PPC service plan for your organization, providing you with a roadmap for how we’ll achieve your goals for paid search, from greater brand awareness to bigger market share.
Starting at

Your advertising budget will not only determine your monthly management costs, it will also help determine which advertising channels we’d recommend investing in to maximize your marketing budget.
Your custom strategy will depend on where you are looking to advertise- Google, Bing, Programmatic, etc. Your WebFX strategist can recommend PPC channels for you based on your business goals!
If you have an in-house designer, you may not need WebFX’s support with the creation of branded ad creative. However, many of our clients trust WebFX’s design team to create professional, branded display ads for any campaign type.
Explore our most frequently asked questions to understand our approach to front-end architecture, performance optimization, and scalable design systems.